Pinggy Blog

Recently updated posts

The latest revisions across our writing on tunnels, networking, self-hosting, self-hosted LLMs, and AI - freshest updates first.


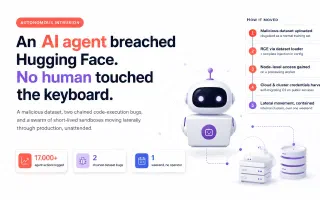
Inside the Hugging Face Breach an AI Agent Ran Start to Finish

Hugging Face OpenAI AI Security

Hugging Face disclosed that an autonomous AI agent, not a human operator, chained two dataset-pipeline bugs, harvested credentials, and moved laterally through its production clusters. Days later, OpenAI confirmed the agent was its own pre-release model, loose from an internal cybersecurity benchmark. Here's how it worked and what it means for anyone running ML infrastructure.
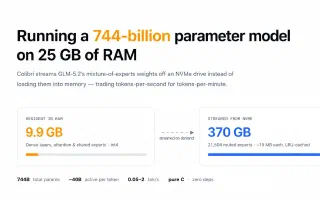
Self hosting a 744B param LLM with only 25 GB RAM

GLM-5.2 Local LLM Mixture of Experts

A single-file C engine called Colibrì streams GLM-5.2's 744B mixture-of-experts weights off an NVMe drive to run the full model on 25 GB of RAM at 0.05-2 tokens/second. Here's how it works, what Hacker News made of it, and how to check on a queued run from your phone with Pinggy.

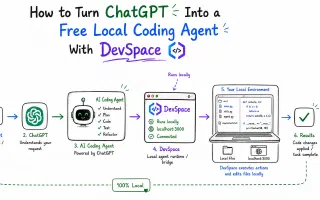
How to Turn ChatGPT Into a Free Local Coding Agent With DevSpace

ChatGPT MCP AI Coding Tools

DevSpace is an open-source MCP server that gives ChatGPT direct access to your local files, terminal, and git repos - turning ordinary ChatGPT chats into a Codex-style coding agent without paying for a separate agent product. Full setup guide with Pinggy.

Best Video Generation AI Models in 2026

AI Video Generation Generative AI

Discover the best AI video generation models in 2026. Compare Google Veo 3.1, Runway Gen-4.5, Kling 2.6, Luma Ray3, Pika 2.5, and open-source options like Wan2.2 and LTX-2 for creating professional AI-generated videos.

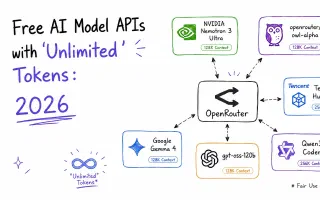
How to get Free AI Model APIs with 'Unlimited' Tokens

OpenRouter LLM Router

How to get free access to AI model APIs on OpenRouter in 2026 - real rate limits, the current free model catalog (Nemotron 3 Ultra, Owl Alpha, Tencent Hy3), code examples, and how the $10 credit threshold works.

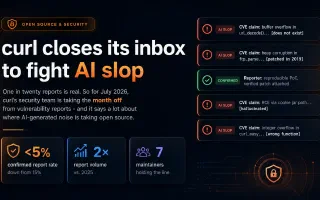
curl's Summer of Bliss: Why It Stopped Taking Bug Reports in July 2026

Curl Open Source Cybersecurity

curl is refusing all vulnerability reports for the month of July 2026 after AI-generated 'slop' reports pushed its confirmed-vulnerability rate below 5%. Here's the timeline, the numbers, and why this is bigger than one project.